Black Wall OS
Privacy-first operating system with hardened kernel and secure enclaves.
Privacy-first operating system with hardened kernel and secure enclaves.
Overview
Privacy-first operating system with hardened kernel and secure enclaves.
Community Stars
9,800
GitHub Stars
Primary Language
C / Rust
Core codebase
Status
Active
Community maintained
License
Open Source
Permissive license
Install the OS
Signed release artefacts, reproducibly built from the tagged source tree.
| Artefact | Target | Version | Size |
|---|---|---|---|
| blackwall-latest.tar.gz | All Systems | v1.0.0 | 12 MB |
Black Wall desktop, live
A guided walkthrough of the hardened desktop session — compositor, terminal, sandboxed file manager, capability settings, and the verified app store.
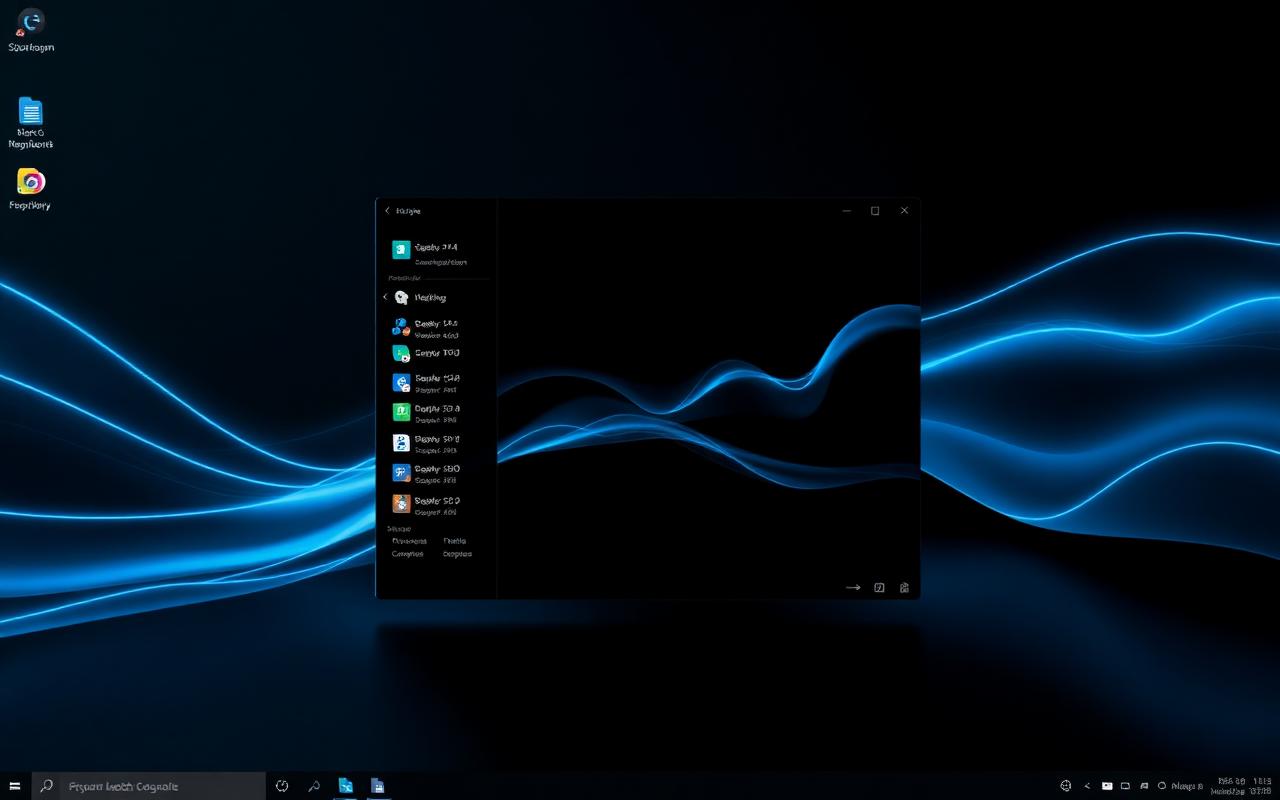
Wayland compositor running on the capability microkernel.
System requirements
- x86_64 or ARM64 CPU with TPM 2.0
- 4 GB RAM (8 GB recommended)
- 12 GB disk for a persistent install
- UEFI with Secure Boot enabled
Capabilities
Capability microkernel
85% smaller trusted surface than a monolithic kernel; drivers run outside ring 0.
Zero unsafe drivers
Rust drivers with formal verification on memory boundaries.
TPM-attested boot
1.2 ms signed boot state validation before any user space starts.
Revocable permissions
Every app permission is a token you can revoke live, mid-session.
Reproducible packages
The store refuses anything that is not byte-for-byte reproducible.
Lockless IPC
0.18 µs message passing keeps overhead under 2% system-wide.
People behind the project

Testers & QA
Nobody listed yet — this project is looking for its first contributors.